

- Authority
- Customer policy
- Provenance
- Prompt submitted
- Event time
- Policy reference
PROMPT-DLP / POC-04
Sovereign AI security · Southeast Asia
Stop sensitive data reaching public AI without sending security data to another cloud.
SentraMind gives security teams a customer-controlled path from signal to deterministic policy decision and inspectable evidence. Platform Core and GenAI Prompt DLP are available for a private proof of concept.
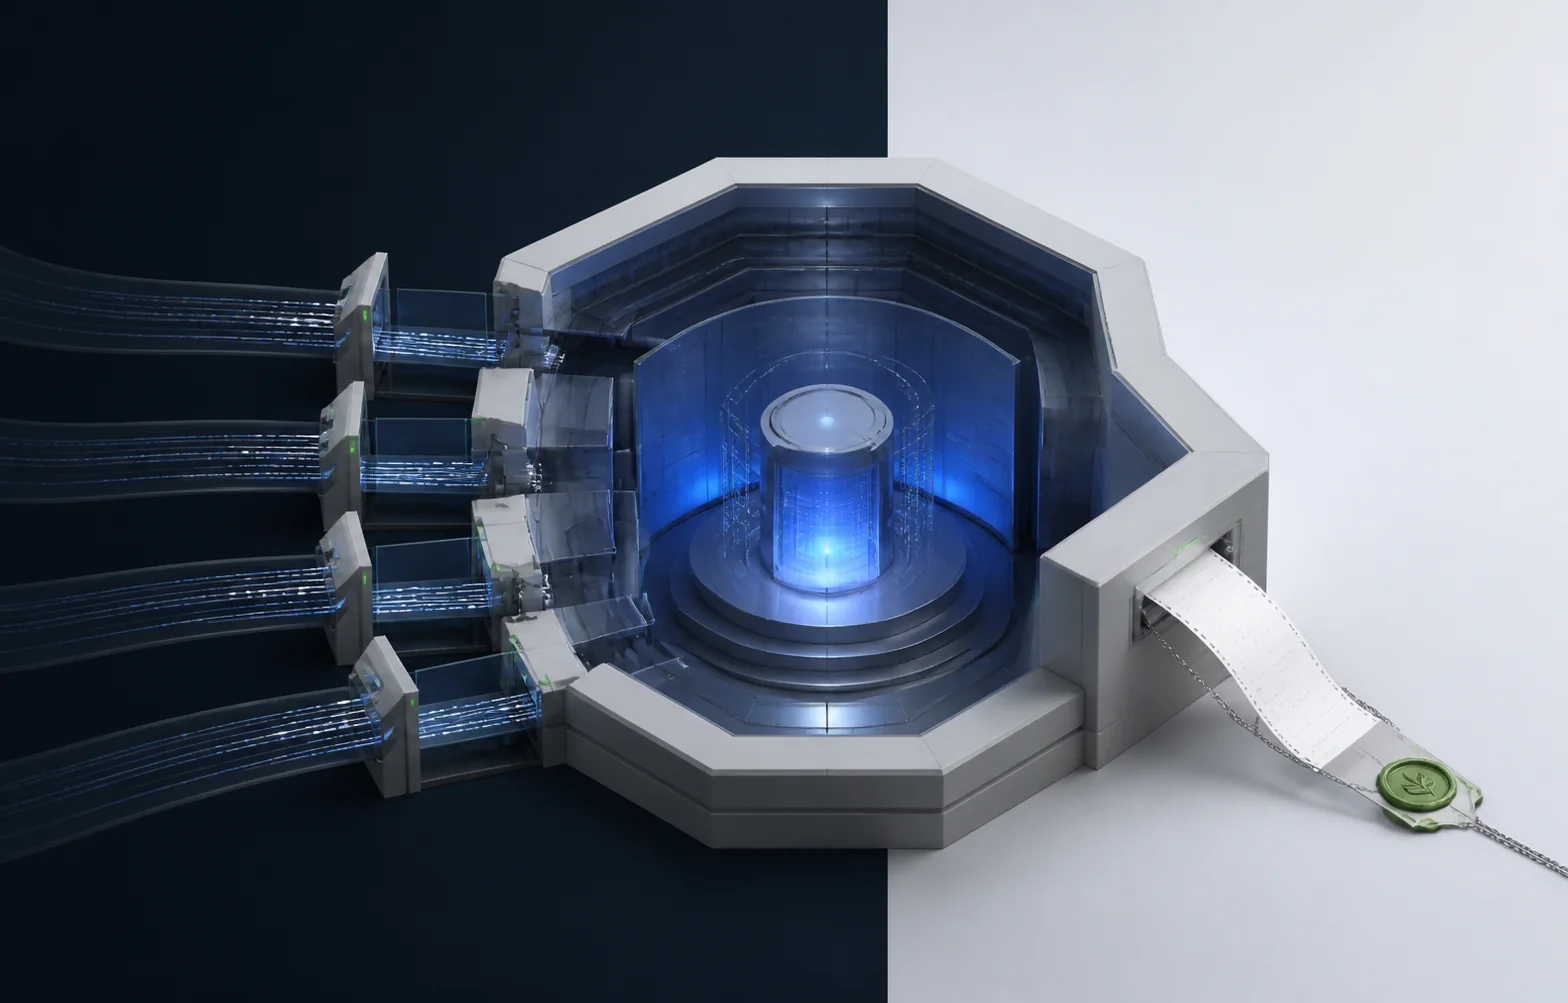
Customer-controlled environment Prompt warned POC example
- Prompt submitted
- Deterministic detection
- Customer policy
- External route stopped
- Illustrative decision receipt
The operating problem
Public AI creates a new path out of your control boundary.
Employees move quickly. Sensitive prompts can include credentials, personal data, source code and operational context before a conventional review process can react. For sovereign and regulated environments, adding another hosted security layer can recreate the same disclosure problem.
- 01 Keep the security decision inside infrastructure you control.
- 02 Make deterministic policy authoritative; model assistance remains subordinate.
- 03 Give reviewers a readable record of what happened and why.
What you can evaluate now
A bounded POC, built around one consequential workflow.
The evaluation is deliberately narrow: prove the boundary, policy path and evidence before expanding scope.
Platform Core
The governed runtime, policy path and evidence foundation used by the POC.
GenAI Prompt DLP · Sentry
Deterministic prompt inspection and customer-defined warn or block outcomes.
AI Usage Observability · Cartographer
Visibility into organisational AI usage is the next planned capability, not part of today’s POC.
From event to evidence
The control path stays understandable under scrutiny.
- 01
Observe
A prompt reaches the controlled inspection point.
- 02
Detect
Deterministic detectors identify policy-relevant content.
- 03
Decide
Customer policy authorises the outcome; assistance cannot overrule it.
- 04
Record
A decision receipt preserves outcome, authority and provenance.
Deterministic browser demonstration
Test the detector layer before the evaluation.
The live demonstrations execute deterministic detector logic locally in your browser. They do not reproduce the appliance, model classification or a production deployment—and they are not evidence of those systems.
Open all live demonstrationsQualified trust evidence
Proof should identify its boundary.
Customer-controlled deployment
Designed for self-hosted and air-gap-capable operation. Final topology is agreed and tested during evaluation.
Authoritative policy path
Deterministic controls and customer policy remain authoritative; model assistance is not permitted to make consequential decisions.
Inspectable records
Current code includes hash-chain and evidence-sealing primitives. A complete end-to-end evidence pipeline remains evaluation work.
First-party portal runtime
This portal is built without hosted fonts, analytics or third-party runtime assets. Deployment network behaviour is verified separately.
The signature artifact
Every governed outcome should end in a receipt a reviewer can interrogate.
A decision receipt makes the policy authority, source, event time and integrity state explicit. The example shown here is synthetic and demonstrates the intended evidence grammar—not a certificate and not a production event.
- Authority
- Customer policy
- Provenance
- Prompt submitted
- Event time
- Policy reference
PROMPT-DLP / POC-04
Capability horizon
A focused product now; a governed crew over time.
Cartographer is coming next. The remaining specialist concepts—from email and source-code review to vulnerability and incident workflows—belong to the M3–M9 design-partner roadmap. They are published to guide discovery, not represented as available features.
Explore the Crew roadmap → Available for POC Platform Core + Sentry Coming next Cartographer Design-partner roadmap Crew M3–M9
Built for regional operating reality
Start with sovereignty requirements, not a generic cloud assumption.
The evaluation conversation covers site constraints, disconnected operation, ownership of policies and evidence, and the regulatory context relevant to Southeast Asian public-sector and regulated buyers. Regulatory material supports discovery; it is not legal advice.
Review regional contextA private, evidence-led evaluation
Bring the boundary, workflow and acceptance criteria that matter to your team.
We will scope a POC around GenAI Prompt DLP, identify what your environment must provide, agree measurable acceptance criteria and document what is current, illustrative or still to be built. Your security, architecture and procurement stakeholders leave with one shared record of the evaluation boundary.