

Sensitive by nature
Source code, email, identities, configurations, database details and incident records are routine security inputs.
Platform · Private AI Core
A customer-controlled reasoning service for every SentraMind agent crew—deployed inside your environment, sized to your workload, and designed to operate without a hyperscale GPU cluster.
The model assists interpretation. Source systems, deterministic controls and authorized people remain authoritative.
Design-partner roadmap This build contains no model runtime and calls no model — every model-shaped capability reports an explicit “model not configured” state. The architecture, model classes and hardware figures on this page are intended design and sizing targets: not measured results, and not a supported production specification.
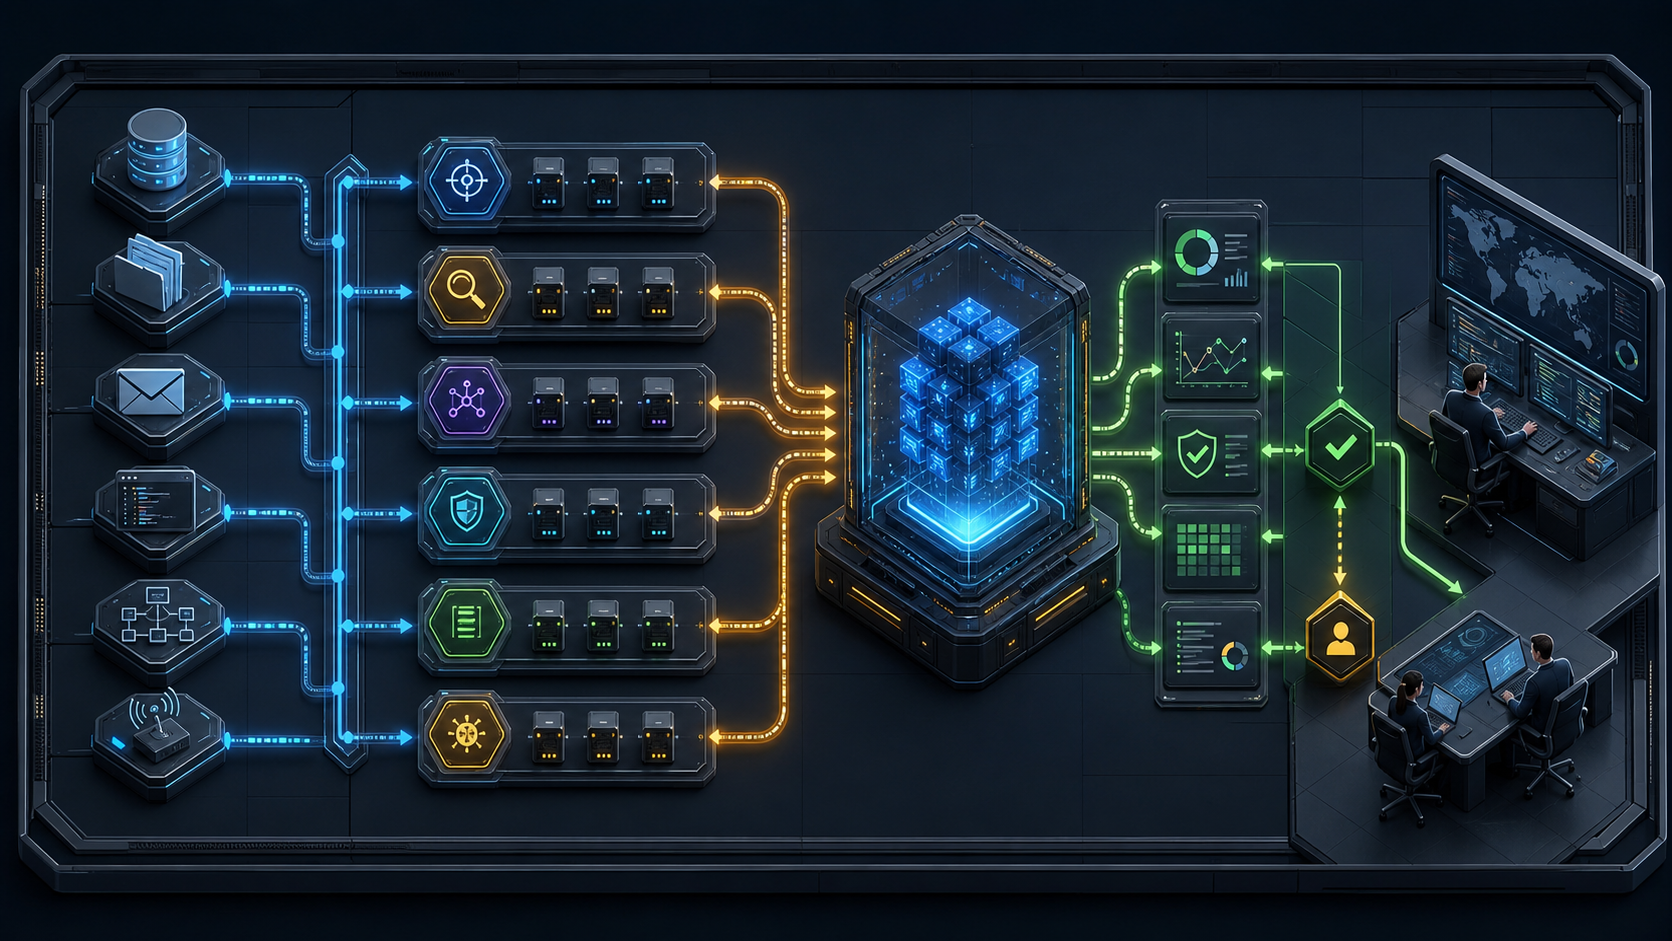
Raw stores remain authoritative. Agents send only the evidence needed for an approved task through policy and access controls.
Customer-controlled environment · no public AI service required for normal private inference
An approved user or agent crew opens a defined security task.
Parsers and deterministic detectors select the smallest relevant context.
Access checks, redaction, purpose rules and retrieval permissions are enforced.
The approved model and private knowledge service analyze a bounded request.
Structured output is checked by policy-controlled and deterministic services.
Authorized people decide; evidence references, versions and outcomes are auditable.
Why private
Investigation evidence can contain material that should not be submitted to an uncontrolled external service.
Source code, email, identities, configurations, database details and incident records are routine security inputs.
Prompts, retrieved knowledge and responses can remain within the deployment boundary and customer retention policy.
Restricted-network and isolated operation can be designed with approved offline updates.
Shared service
Specialists use a common governed vocabulary and reasoning service without receiving unrestricted access to one another’s sources.
Explains possible internal or unintended email data exposure using selected message evidence.
Interprets code and application findings, relates security references and drafts remediation guidance.
Connects relevant events across approved log sources and prepares investigation narratives.
Future specialists connect through the same authenticated gateway, purpose controls and audit trail.
Practical baseline
A planning baseline balances analysis quality, response time, concurrency, power and acquisition cost. Final capacity is established by testing.
Quantized 12–14B model, one 24–32 GB GPU, 128 GB RAM and 2 TB NVMe.
Recommended planning baseline—not a performance guaranteeQuantized 24–32B model on a 48 GB ECC GPU with 128–256 GB RAM.
For stronger reasoning or moderate concurrencyTwo GPUs or independent nodes where redundancy, separation or higher concurrency is required.
Availability is optional and workload-ledData residency
The deployment statement records the final retention, audit and export policy; these are the architectural defaults.
Raw logs, mail stores and repositories remain in their authoritative source systems.
Only approved, minimized evidence enters private inference; credentials and secrets are excluded or masked.
Approved internal knowledge is indexed privately and retrieval preserves source access rules.
Prompts and responses follow customer retention; support exports require approval; training is disabled unless separately governed.
Implementation journey
The engagement proves fit before production acceptance instead of treating a model name as the solution.
Confirm tasks, languages, boundaries, concurrency, context, response targets and existing infrastructure.
Benchmark candidate models and hardware, then install the approved release inside the controlled environment.
Connect approved crews, identity and knowledge; complete security, functional and performance acceptance.
Monitor quality, apply controlled updates and retain tested rollback paths through the managed lifecycle.
Platform · Private AI Core
The assessment defines the deployment class, model class, tested capacity envelope, availability design and implementation scope before hardware is committed.