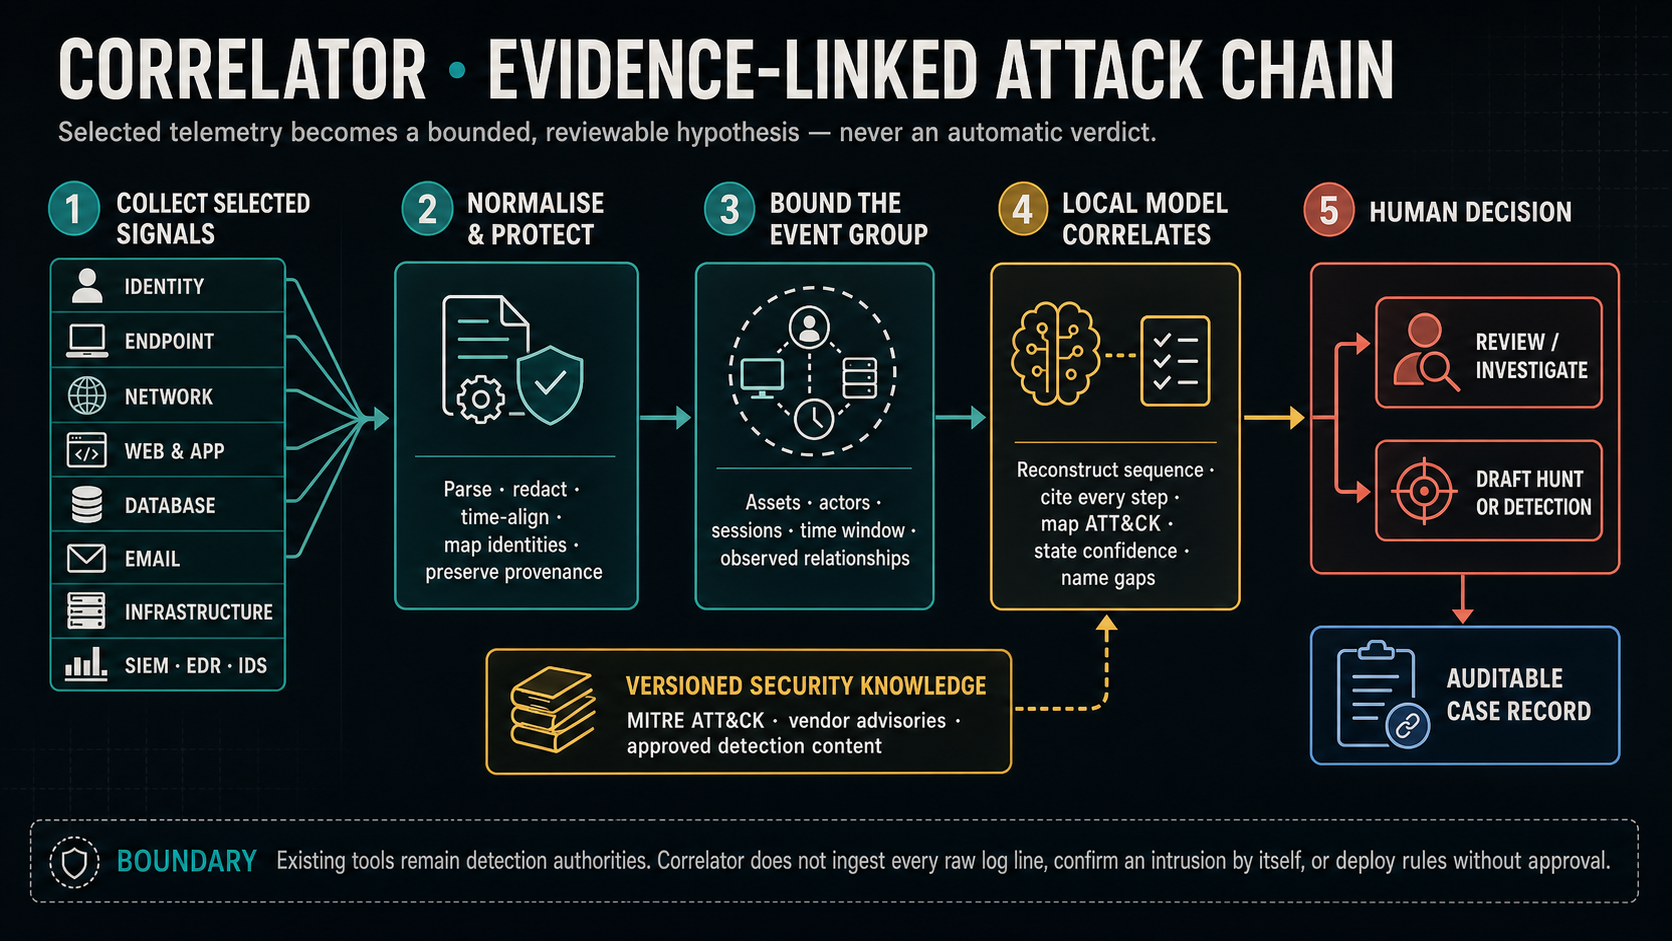
Source family Common sources Signals we can correlate
Identity & access Active Directory, domain controllers, Windows logon events, LDAP, Kerberos, RADIUS, SSO/MFA, PAM and VPN concentrators Sign-in success/failure, ticket use, account and group changes, privilege elevation, MFA events, impossible travel and unusual access paths
Endpoints & servers Windows Event Log, Sysmon, Linux auditd/journald/syslog, Unix auth logs, EDR/HIDS findings and file-integrity monitors Process and service creation, command lines, file/registry changes, scheduled tasks, network connections, device events and sensor health
Network & perimeter Firewalls, IDS/IPS, routers, switches, wireless controllers, NAC, DNS, DHCP, VPN, proxy, secure web gateway and NetFlow/IPFIX Connections, denies, DNS queries, address leases, remote sessions, beacon timing, east-west movement and unusual transfer patterns
Web, API & applications IIS, Apache, NGINX, reverse proxies, load balancers, WAF/API gateways, application audit logs and framework logs Requests, status codes, routes, sessions, authentication/authorisation failures, admin actions, data export and application-specific security events
Databases & data platforms Microsoft SQL Server, Oracle, MySQL/MariaDB, PostgreSQL, MongoDB, Elasticsearch and database activity monitoring Authentication, privileged queries, schema or permission changes, bulk reads/exports, failed access and audit-policy changes
Email & collaboration Exchange Server, mail-transfer and secure-email gateways, Postfix, Sendmail, Exim, Dovecot, Zimbra and collaboration audit feeds Message trace, authentication, forwarding-rule changes, mailbox access, administrative actions, delivery anomalies and suspicious-link or attachment metadata
Infrastructure & platforms VMware vSphere/ESXi, Hyper-V, Kubernetes audit, containers, Docker, storage/NAS, backup platforms and hypervisor management Administrative actions, workload lifecycle, configuration changes, image or secret access, backup deletion and control-plane activity
Security controls SIEM alerts, EDR/XDR, NDR, IDS/IPS, DLP, WAF, vulnerability scanners, malware sandboxes and threat-intelligence platforms Normalized findings, detection metadata, severity, disposition, affected entities, indicators and links to the authoritative source alert
Physical, OT & custom systems Badge/access control, building systems, industrial gateways, historian alarms, ERP/CRM and customer-built applications Physical access, operator actions, alarms, transaction anomalies and domain-specific audit events; custom mapping and validation are required
Coverage categories and logging principles are informed by MITRE ATT&CK detection knowledge, OWASP security-logging guidance, NIST log-management guidance and vendor documentation. These sources guide schemas and evaluation; they do not turn model output into authoritative evidence.